Key Takeaways
- SSL stripping is an MITM attack that downgrades HTTPS connections to insecure HTTP, allowing attackers to steal data intended for users.
- Risks of SSL attacks include credential theft, exposure of sensitive data, altered communications, and fraudulent purchases. In severe cases, consumer data breaches and identity theft may occur.
- SSL stripping attacks can be hard to detect, since the malicious website URL and page design are usually a close match to the intended site.
- To detect and prevent SSL stripping attacks, prioritize HSTS-enabled browsers, HTTPS site connections, secure Wi-Fi or wired network connections, and advanced network security solutions such as the SecureW2 JoinNow Platform.
When you visit a website, you typically see a little padlock on the left side of the URL address bar. That symbol — or something similar, depending on the browser — indicates a secure connection under Hypertext Transfer Protocol Secure (HTTPS).
Normally, under Hypertext Transfer Protocol (HTTP), data is sent in plain text, which could let a hacker intercept sensitive data like passwords. With HTTPS, however, an added encryption layer via the Transport Layer Security (TLS) protocol protects the HTTP traffic.
Nowadays, browsers and websites default to HTTPS, even if you enter http:// vs. https:// as a prefix. But a cyberattack called SSL stripping can override this default security mechanism, forcing you to use unencrypted HTTP communication.
Here, we’ll take a closer look at what SSL stripping is, how an SSL stripping attack works, and ways to prevent those attacks.
What Are SSL Stripping Attacks?
SSL stripping attacks are a type of man-in-the-middle (MITM) cyberattack that downgrades an HTTPS connection attempt to HTTP by blocking or modifying redirect responses. They’re often called HTTPS downgrade attacks because they downgrade from HTTPS to HTTP.
The SSL here stands for Secure Sockets Layer, a deprecated security protocol to encrypt data transmitted between web browsers and web servers.
Although the term “SSL stripping” remains common, modern implementations actually target TLS instead. That’s because TLS has replaced SSL, thanks to enhanced encryption and authentication, advanced ciphers and more robust security.
Despite the underlying protocol shift, the term “SSL stripping” has stuck; modern SSL stripping simply prevents TLS encryption instead.
See your security gap before attackers do.
See continuous trust in action on a platform that includes RADIUS, PKI and AI security.
How Does SSL Stripping Work?
In an SSL stripping attack, when users connect to a website, a bad actor intercepts the connection and “strips” the SSL (or now TLS) request, causing the server to deliver an unencrypted HTTP connection instead of a securely encrypted HTTPS connection. As a result, the user intends to visit an HTTPS webpage but is sent to a malicious HTTP site instead.
This requires the attacker to gain an on-path position between the victim and the website, allowing them to intercept and modify traffic in transit. Tools such as SSLstrip can automate this downgrade once the attacker achieves on-path positioning.
More specifically, SSL stripping involves the following steps:
- Attacker gets in the middle of the victim and the website
- Victim requests a website via HTTP
- Attacker blocks victim’s HTTPS upgrade, downgrades to HTTP connection
1. Attacker Gets in the Middle of the Victim and the Website
The hacker first needs to launch an MITM or adversary-in-the-middle (AitM) attack, such as Address Resolution Protocol (ARP) spoofing or a rogue access point.
For example, on a corporate network, an attacker might trick your laptop into thinking their device is the router, while tricking the router into thinking their device is your computer. Or, on public Wi-Fi, a hacker might set up a fake Wi-Fi network that resembles the correct one.
This image of an AitM attack shows an attacker intercepting a user’s access to a website:
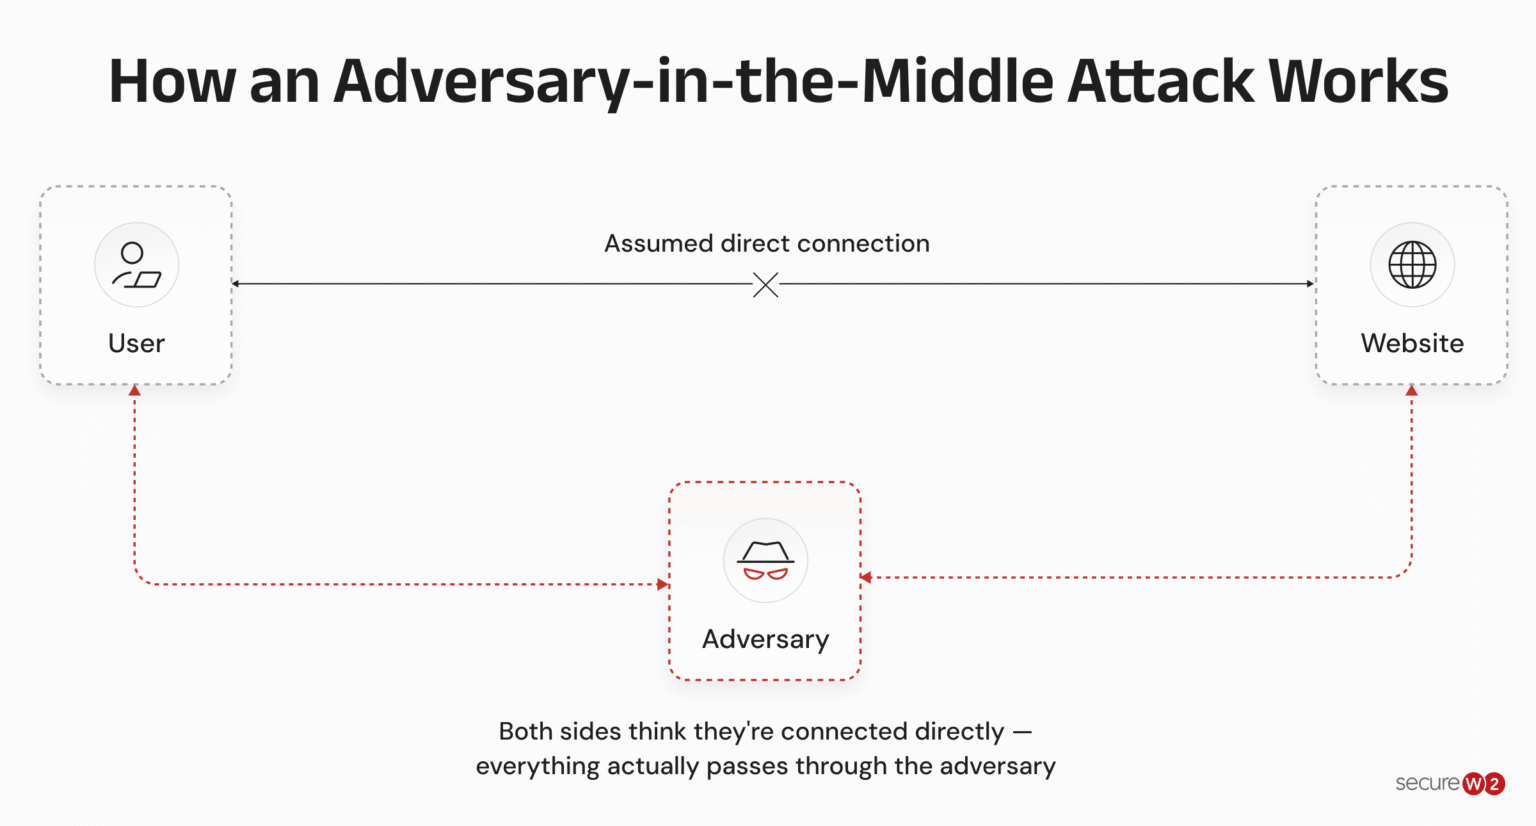
From there, the attacker can relay data between the victim and the website while potentially reading it in plain text, if they can implement additional steps below.
2. Victim Requests a Website via HTTP
For an SSL stripping attack to work, the browser must have an opportunity to connect over HTTP before switching to HTTPS.
Many websites use HTTP Strict Transport Security (HSTS), defined in RFC 6797, which tells browsers to connect over HTTPS automatically. However, if a website doesn't use HSTS, or a user visits a site for the first time and the domain isn't on the browser's HSTS preload list, the browser may initially attempt an HTTP connection.
This can happen when a user enters a website address without specifying http:// or https://, or explicitly starts with http://. In these cases, an attacker positioned between the user and the website may have an opportunity to interfere with the connection.
3. Attacker Blocks Victim’s HTTPS Upgrade, Downgrades to HTTP Connection
If the browser attempts an HTTP connection, the attacker can intercept the website's redirect to HTTPS and prevent the upgrade. The victim's browser then communicates with the attacker over HTTP, while the attacker connects to the legitimate website over HTTPS.
Because the connection between the victim and the attacker isn't encrypted, the attacker can read or modify the data the victim sends, including login credentials and other sensitive information. The attacker can still communicate with the legitimate website over HTTPS, making it possible to relay requests and responses without the victim realizing their connection has been compromised.
Even when an SSL stripping attack succeeds, the browser won't display the padlock or secure-connection symbol because the victim's connection uses HTTP. Spotting the missing indicator can alert the victim to the risk before they enter sensitive information.
Where SSL Stripping Happens
SSL stripping attacks commonly occur on public Wi-Fi networks — open, unsecured networks accessible to anyone. Attackers create spoofed wireless networks and hotspots, boosting the signal to trick users and devices into connecting.
Once a device connects to the untrusted network, attackers can control web traffic and steal data from connected users.
Devices set to auto-connect can join a spoofed Wi-Fi network without the user ever taking an action — attackers boost the malicious network’s signal specifically to trigger this.
“Wi-Fi is just a flawed protocol in that if your laptop or your phone sees the name of a Wi-Fi network that you've connected to before and it's a strong signal, it's just going to start trying to connect to it. And when it tries to connect to it, it's going to send its credentials; it's going to send its password. That's a problem because now a hacker has a great way to steal credentials."
Micah Spady, Director of Product Marketing at SecureW2
But SSL stripping doesn’t require a Wi-Fi connection. Many other types of MITM attacks allow hackers to redirect users to fake sites.
Let’s explore the most common forms of SSL stripping.
Types of SSL Stripping Attacks
Common MITM attacks with SSL stripping include:
- ARP spoofing: Also called an ARP poisoning attack, this cyberattack lets attackers spoof a user’s IP address with forged ARP packets that point to the attacker’s Media Access Control (MAC) address.
- Proxy servers: With proxy servers, attackers can redirect a user’s browser traffic to their own server instead of the user’s intended destination. This allows them to intercept user data.
- Spoofed public Wi-Fi networks: Attackers create public Wi-Fi networks with names similar to nearby trusted networks. Signal boosting encourages devices to automatically connect to the malicious network instead, giving the attacker access to all network traffic and data.
Top Risks of SSL Stripping Attacks
SSL stripping attacks pose serious risks to individuals and companies, including:
- Credential theft: When attackers intercept traffic, they can access all transmitted data, including login credentials submitted by unsuspecting victims.
- Sensitive data theft: With access to login credentials and private data in transit, attackers can steal personal and company data, including financial records, communications, and intellectual property.
- Consumer data breaches: Corporate attacks may also expose sensitive consumer data, undermining trust and potentially leading to legal consequences.
- Falsified communications: Attackers can do more than just see your data; they can alter it, too. They may send inaccurate or malicious content, including harmful prompts and links that do more damage than the original attack.
- Fraudulent purchases: With access to your financial logins, attackers can use your accounts or credit cards to make withdrawals or purchases.
- Identity theft: Using personally identifiable information (PII), such as your full name, date of birth, and Social Security Number, attackers can set up fraudulent accounts with stolen user data.
Does SSL Stripping Still Work in 2026?
Yes, SSL stripping still works today — although most modern references to SSL, including SSL certificates, actually use TLS instead.
The prevalence of HSTS has helped reduce the effectiveness of SSL stripping. Some browsers even preload the HTTPS versions of certain websites before a user ever visits.
However, not all websites use HSTS, and not all browsers have the same protections enabled. If an attacker can intercept a connection before HTTPS is established, SSL stripping may still succeed.
For example, an attacker on a public Wi-Fi network might use ARP spoofing to intercept a device's network traffic. They could then attempt to manipulate the victim's web requests or redirect them to a lookalike domain that lacks adequate HTTPS protections. The success of this approach depends on the site's configuration, the browser's security features, and whether the attacker can successfully intercept the connection.
The security plan that scales with you.
Our solutions can scale from mid-market to global enterprises. Compare options and see how our solutions protect you from costly breaches and ensure peace of mind.
How To Detect and Prevent an SSL Stripping Attack
Preventing SSL stripping attacks — and detecting active attacks — requires a multi-layered approach. Some of the responsibility falls on website owners and enterprise IT, but individual users also play a role.
Consider the following steps to protect against SSL stripping, starting with individual users and employees, then moving on to IT teams and website owners.
Everyone (Individual Users, Employees)
You don’t need technical expertise to protect yourself from SSL stripping; a few simple browsing habits go a long way.
1. Use an HTTPS-First Browser
Choose a browser that defaults to HTTPS, so attackers never have a chance to intercept an HTTP request.
2. Check for a Secure HTTPS Connection
Even with an HTTPS-first browser, always check for the padlock or similar indications that your own HTTPS connection is valid and secure.
3. Avoid Wi-Fi Hotspots and Public Wi-Fi
Wi-Fi hotspots and public Wi-Fi are highly susceptible to SSL stripping attacks. With near-identical network names and signal boosting, user devices may automatically connect to malicious networks.
If you can’t avoid these connections, use a virtual private network (VPN) for an extra layer of encryption.
4. Obey Browser Warnings
Pay attention to all browser warnings. If the browser tells you a site is unencrypted or not a trusted site, don’t proceed — back out.
5. Know the User-Specific Signs of an SSL Stripping Attack
You should suspect possible SSL stripping if:
- You expect an HTTPS web page, but it loads with http:// instead
- Your browser shows a warning for an insecure connection or untrustworthy web page
- Your browser’s symbol of a secure connection (usually a padlock) is missing
- A site that operates as expected on a secure network responds differently on an unsecured network
IT & Website Owners
While users can reduce their own exposure, only administrators can close the gaps that make SSL stripping possible in the first place.
1. Enable TLS Sitewide Across All Domains
It doesn’t matter what your site is for, how it functions, or whether or not it processes credentials or sensitive information. Today, it’s best practice to serve all pages on all websites over TLS (commonly called SSL) for secure HTTPS connections. This is one of the best ways to prevent SSL stripping attacks.
2. Implement HSTS Pre-Loading on BYOD and Managed Devices
In addition to default TLS settings, you should enforce HSTS across all devices and browsers — including browser settings on bring-your-own-device (BYOD) devices.
With HSTS preloading, browsers will not connect with HTTP requests — only HTTPS.
3. Enable Secure Cookies for Users & Devices
Secure cookies can only transmit data over HTTPS, so attackers will never receive them over unsecured HTTP connections. Enable these by default across all browsers and devices.
4. Educate Users on MITM Attacks, Including SSL Stripping
Train employees to prevent and detect SSL stripping attacks. They should know best practices (including using a VPN over public Wi-Fi) and be able to recognize the signs of a potential SSL stripping attack.
5. Know the Site and Network Signs of an SSL Stripping Attack
Site and network administrators should suspect SSL stripping if:
- You notice unexpected redirects
- You see HTTP traffic for HTTPS domains
- Users report unusual login pages, prompts, or authentication processes
6. Use Automated Solutions for Reliable, Updated Protection
User and administrator awareness is key, but manual prevention and detection techniques are only part of the solution. Today, automated products and services can handle it all: secure settings, network monitoring, threat detection, and instant revocation.
So don’t leave your network security up to chance. Use modern automated solutions for simpler security that saves time and reduces stress.
Protect Against SSL Stripping With SecureW2
Browser protections help prevent SSL stripping, but securing the network itself adds another layer of defense. By preventing unauthorized devices from connecting and helping employees verify legitimate enterprise networks, you can reduce opportunities for attackers to intercept network traffic.
JoinNow Cloud RADIUS simplifies certificate-based network authentication. With 802.1X EAP-TLS, devices and networks mutually authenticate using digital certificates, helping prevent unauthorized access and reduce the risk of connecting to rogue networks.
JoinNow Dynamic PKI automates certificate issuance and lifecycle management, making it easier to maintain secure authentication as devices are added, updated, or removed.
Ready to strengthen your network security with automated, certificate-based authentication? Schedule a demo today.
Frequently Asked Questions
What's the difference between SSL stripping and SSL hijacking?
SSL stripping downgrades a connection from HTTPS to HTTP so traffic is never encrypted, while SSL hijacking intercepts an encrypted session — typically by presenting a forged certificate so the attacker can decrypt traffic in transit. In stripping, the victim has no secure connection at all; in hijacking, the victim has a secure connection to the wrong party. Both are man-in-the-middle attacks, but they exploit different weaknesses.
Does a VPN prevent SSL stripping?
A VPN largely neutralizes SSL stripping on untrusted networks. Because all traffic travels through an encrypted tunnel to the VPN server, an attacker on the local network — like spoofed public Wi-Fi — can't see or modify your web requests. However, a VPN only protects the path it covers; traffic between the VPN server and the destination site could theoretically still be downgraded, so HTTPS and HSTS remain important.
Can SSL stripping steal passwords?
Yes, credential theft is the main goal of most SSL stripping attacks. Once an attacker downgrades a connection to HTTP, anything the victim types into a login form, including usernames and passwords, is transmitted in plain text that the attacker can read. That's why sites that handle logins should enforce HTTPS with HSTS, and why users should never enter credentials on a page without a secure-connection indicator.
Does HSTS completely prevent SSL stripping?
HSTS significantly reduces the risk but doesn't eliminate it. A site's HSTS policy only takes effect after a browser's first visit, leaving a "first-visit gap" that attackers can exploit — unless the domain is on the browser's HSTS preload list, which closes that gap. Sites that don't implement HSTS at all, or misconfigure it across subdomains, remain vulnerable.
